Separate networks deliberately
Workstations, guests, IoT and administration get appropriate boundaries. Permitted connections and responsibilities are documented.
Protect networks, organise access and reduce practical risks in everyday operation.
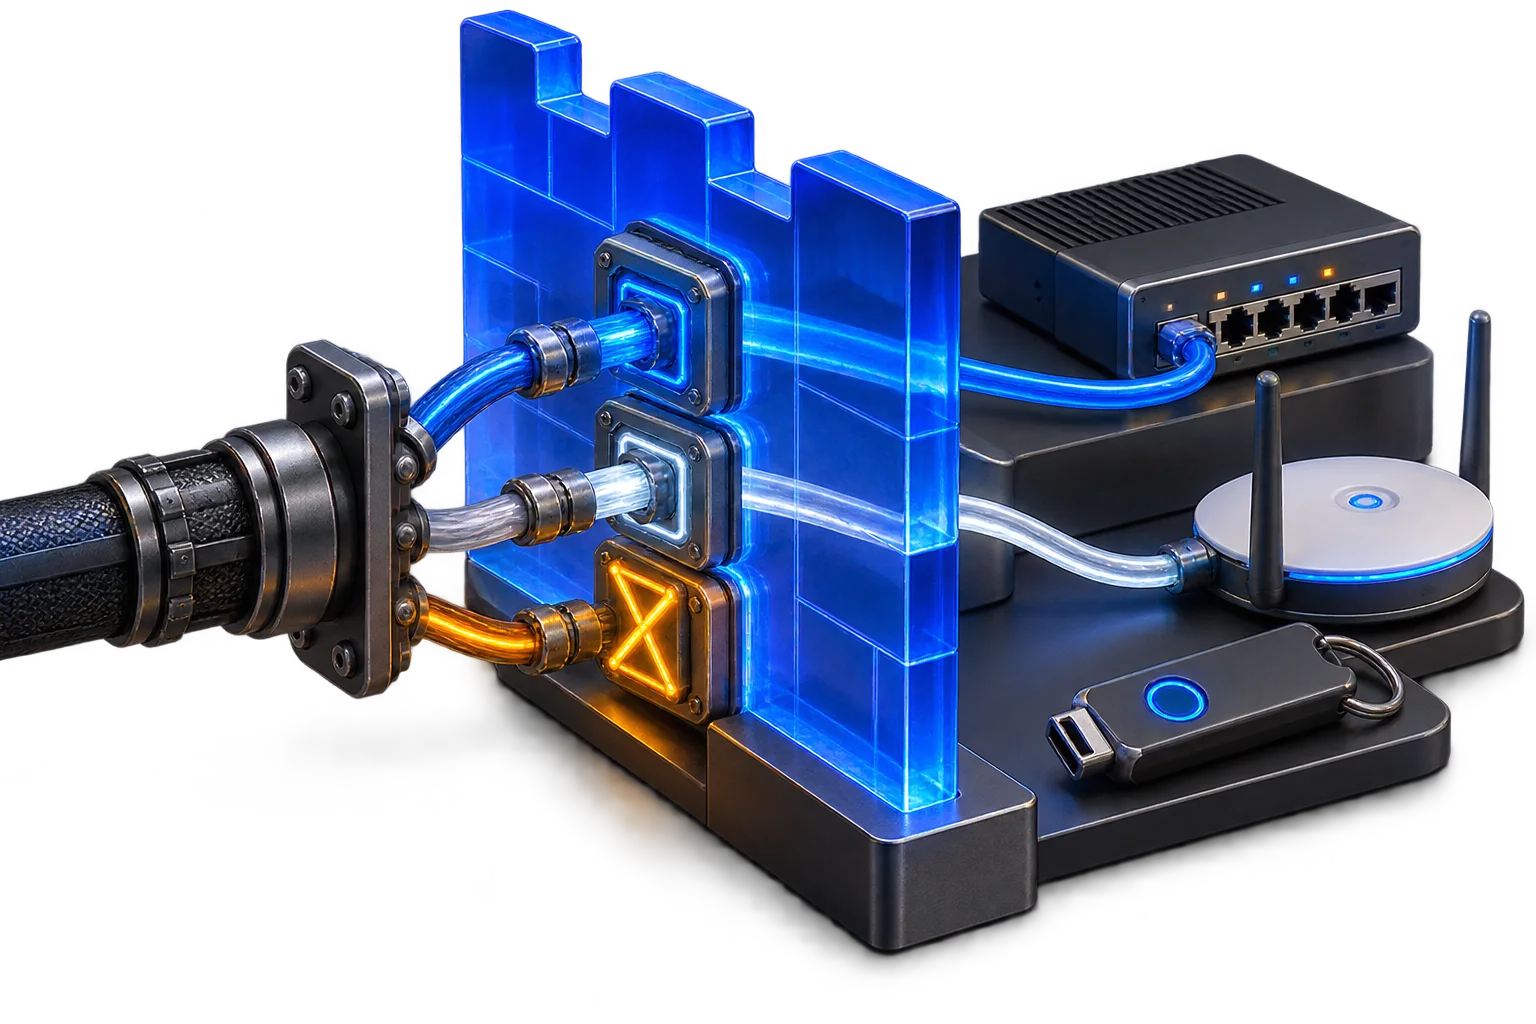
We assess the starting point and implement agreed safeguards: understandable firewall rules, separated network segments, protected remote access and clear administration. Changes are planned with a documented way back.
Protection comes from suitable settings and an understandable operating model. We look at connections between devices, services and people and focus on practical safeguards for your environment.
What you receive
Zones & allowed connections
VPN · permissions · MFA
Updates · logs · review
The specific scope is shaped around your environment and agreed together before work begins.
Workstations, guests, IoT and administration get appropriate boundaries. Permitted connections and responsibilities are documented.
Remote access, administration interfaces, permissions and multi-factor authentication are reviewed and adjusted by agreement.
Updates, logging, configuration backups and recovery paths are considered together. New rules are checked step by step.
These examples illustrate possible starting points. We use your actual situation to develop a suitable solution.
Clearer structure and rules for a network extended over time.
A suitable VPN path instead of unnecessarily exposed management services.
Useful separation for devices and visitors without unnecessary everyday friction.
A good network is only the beginning. When devices, data and software work together, you get a solution that holds up in everyday life. We consider use, responsibilities and the next steps after handover alongside the setup itself.
We listen and establish your goal, existing setup and actual needs. The people affected, dependencies and known constraints are part of the starting point.
You receive a clear proposal with a defined scope and sensible priorities. Requirements, possible interruptions and responsibilities are discussed in advance.
We configure, integrate or develop the agreed solution and check relevant functions. Specialist work and additional changes are coordinated for the project.
Documentation, an introduction and a clear handover keep the system understandable. Further development, maintenance or ongoing assistance can be arranged individually.
Usually not. We review existing components and prioritise suitable improvements.
Some changes can interrupt connections. Sequence, maintenance window and rollback are agreed in advance.
No. We address agreed risks and explain the limits, remaining work and responsibilities.
Many tasks connect with other areas. These services can complement your project.
Dependable Wi-Fi, structured cabling and networks designed for your spaces and requirements.
03Centralised data, dependable systems and a backup approach that plans for recovery.
10A structured assessment with clear findings and practical next steps.
A specific problem, a new project or simply a good idea. Tell us what you want to achieve and what technology is already in place. Together we will find a suitable starting point.